HackerOne rankingBrazil
Top 2
among researchers in Brazil in 2026
- 2026
- 2nd place in Brazil
- 2025
- 3rd place in Brazil
- Bug bounty
- more than 1 million earned
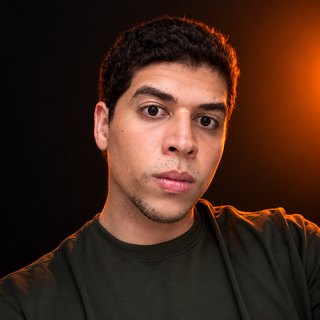 Lucas SouzaCo-founder, Chief Offensive Security
Hify AttackHify Defense
Our technology tests your sites and APIs like a top-tier attacker. In your code, every change is reviewed with context before it reaches production.
Read another account's invoiceGET /api/invoices/demo-02
Decision: Reproducedgoes to the researcher
Open the internal panelGET admin.example.com
Decision: Blockedoutside the authorized scope
Use the session after logging outPOST /api/logout
Decision: In validationwaiting for the researcher
Test the search fieldsGET /api/search
Decision: Queuedwaiting for your approval
[02] Proof
Findings are reviewed by researchers recognized by Apple, Microsoft and Google.
HackerOne rankingBrazil
Top 2
among researchers in Brazil in 2026
Lucas SouzaCo-founder, Chief Offensive Security
Hall of Fame

Companies our team has reported vulnerabilities to
[03] Products
01for your applications and APIs
AI agents test the sites and APIs you authorized. Every finding arrives reviewed, with reproducible proof.
Explore Attack02for your code
Reviews every code change with context and suggests the fix right in the pull request.
Explore DefenseHify Attack for your applications and APIs Product 1 of 2
[04] How it works
AI agents attack the sites and APIs you authorized.
Every finding goes through a person before it reaches you.
The finding includes the steps to reproduce and to fix it.
We repeat the attack to confirm the flaw is closed.
Start with one application. The others come later, in the risk order you define.
[05] Cadence Hify Attack
Your application changes every week. At Hify, every relevant change triggers a test.
PCI DSS v4.0.1, req. 11.4, requires a pentest at least every 12 months and also after any significant change.
[06] Finding Hify Attack
No list of alerts. Your team gets what was exploited, how to fix it, and confirmation that the fix worked.
Read access to another account's data
Severity: HighAccount A read account B's data.
Request made by account A
GET /v1/accounts/7f3c…e21
Authorization: Bearer ‹account A›
Response with account B's data
200 OK
{ "nome": "Mar*** S***",
"cpf": "***.***.***-12" }Check that the account belongs to whoever is asking, before responding.
Suggested snippet
if (account.owner !== user.id)
return 404Fixed on Sep 25 · confirmed by the same attack
Before200 OK
After404
[07] Platform Hify Attack
The board sees whether risk is going down. The technical team sees what to fix first.
Open risks per month
Hify Defense for your code Product 2 of 2
[08] Code review
Defense reads the change together with the services it touches and explains the risk to its author, before production.
Pull request #128 Invoices endpoint
Fixed before production
src/api/invoices.ts lines added: +5
export async function getInvoice(req, res) {const invoice = await db.invoices.find(req.params.id); if (invoice.accountId !== req.session.accountId) { return res.status(403).end();}return res.json(invoice);}Hify Defense bot
This route returns the invoice without checking whether it belongs to the logged-in account. Any authenticated user can read another account's invoice by changing the id.
Suggested fix
if (invoice.accountId !== req.session.accountId) { return res.status(403).end();}Suggestion applied
On the repository you choose.
Explains the risk and suggests the fix where the code is reviewed.
Your developers approve every change before it goes to production.
[09] Control
An autonomous agent is only safe with limits. Yours become policy, checked on every request.
Hosts, routes, test accounts, schedule and speed.
Every request with its response, exportable for audit.
One button on the dashboard stops the run immediately.
Blocked before leaving
Within scope
[10] Radar
Radar monitors in real time more than 200 sources where cybersecurity researchers around the world publish what they find, and works out how each vulnerability affects your applications.
More than 200 sources, in real time.
Every new flaw against your applications.
First, what needs action today.
Flaw lets attackers log in without a passwordCriticalLogin library
Act todayAffects 2 applications
Tampered release steals credentialsHighOpen source package
Does not affect youYou don't use this package
Flaw already used in real attacksHighWeb server
This weekAffects 1 application
Customer data leakMediumThird-party service
Does not affect youYou don't use this service
Flaw exposes another account's dataCriticalAPI framework
Act todayAffects 1 application
[11] Integrations
Also by email, WhatsApp, API, webhooks and single sign-on (SSO).
 Jira
 Slack
 Microsoft Teams
 GitHub
 GitLab
 Claude Code
 Cursor
 Codex
 GitHub Copilot
 Windsurf
[12] Comparison
| Criterion | Annual pentest | Scanner | Bug bounty |  |
|---|---|---|---|---|
| Frequency | Once a year | On every build | While the program runs | In cycles and on every relevant change |
| Finds business logic flaws | Yes | Partial | Partial | Yes |
| Delivers reproducible proof | Yes | Partial | Yes | Yes |
| Reruns the attack after the fix | Partial | Yes | Partial | Yes |
| Fits into your deploy | No | Yes | No | Yes |
| Reviews every code change before production | No | Partial | No | Yes |
| Predictable cost | Yes | Yes | No | Yes |
For internal networks, social engineering and physical testing, traditional pentesting is still the way to go.
[13] Team
Four co-founders building the platform, with an advisor from Nubank's board.
Co-founder, CEO
Founded, scaled and sold Hackr Ads, a platform that managed more than R$ 380 million in ads. Acquired by Conta Simples in 2022.
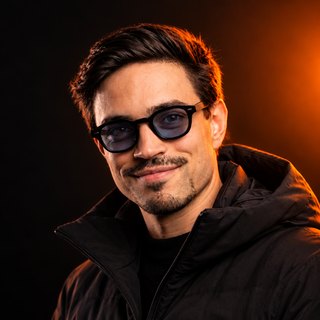
Co-founder, CPO
Experience building AI systems. Security consultant at Dreamer, acquired by Meta in 2026.
Co-founder, Chief Offensive Security
Distinguished hacker, with more than 1 million earned in bug bounties. Top 2 on HackerOne in Brazil in 2026, with experience in DevSecOps teams.
Co-founder, Chief Research & Development
Former developer who worked in AppSec at Mercado Pago, on the team that builds application security solutions for Mercado Livre. Built a proprietary penetration testing harness with Lucas Souza.
Advisor
Member of Nubank's board of directors and chair of its risk committee.

[14] FAQ
For web applications and APIs, Hify tests far more often than an annual pentest, and every finding goes through a specialist. Internal networks, social engineering and physical testing are out of scope: for those, manual pentesting stays in your plan.
No, it complements it. A scanner looks for known patterns, one request at a time. Hify follows multi-step paths with a real session, tests the application's business logic and delivers every finding with proof.
In the environment you define in the scope, with a time window, a requests-per-second limit and destructive methods blocked.
Where it is stored, for how long and who has access are answered in the security questionnaire, under a confidentiality agreement, before any sensitive data is involved. In the evidence, personal data appears masked.
Not to get started. You can begin from the external view or with two test accounts, which already show whether one account can read another's data. Code comes in when you authorize it, and the test then sees more.
No findings does not mean a secure environment. The report records what was tested, with which access, and what was left out and why.
Per application, according to the plan. It depends on each application's complexity, the frequency of cycles and the level of access. The price is set after the demo; there is no public price list.
[15] Contact
A demo with the platform running.
Copy the message below or open your email app. The address is igor@hify.ai.
Or write to igor@hify.ai.